skill · curated · security · mcp · Oct 22, 2026 · 2 min read
snyk/agent-scan: a security scanner for the MCP servers and skills you've already installed
You've installed a dozen MCP servers and Claude Code plugins over the past few months. You ran the /plugin install command from some README, it worked, and you moved on. Do you actually know what any of them can do to your environment?
snyk-agent-scan is Snyk's answer to that question. It auto-discovers every agent config on your machine — Claude Code, Cursor, VS Code Copilot, Windsurf, Gemini CLI — inventories the MCP servers and skill files they reference, and runs a scored risk analysis on each one.
What the analysis covers
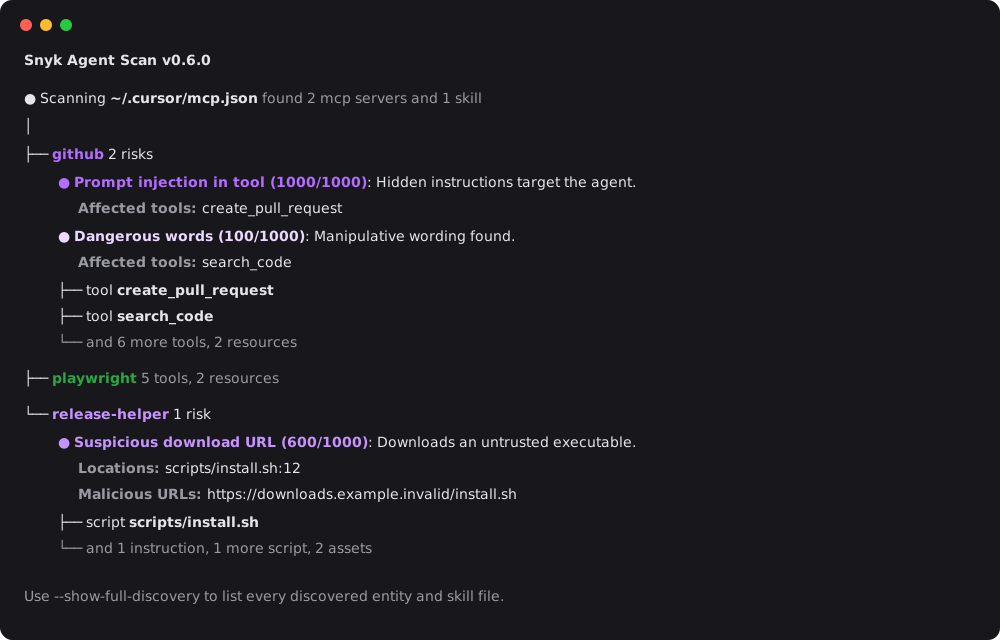
The v0.6+ report format gives you named risk indicators per item: prompt-injection, untrusted-content, private-data, destructive-capability. Each hit comes with an explanation. You can scan your whole machine with a bare uvx snyk-agent-scan@latest, or target one config file, or feed it a single skill file directly: uvx snyk-agent-scan@latest ~/path/to/my/SKILL.md.
Because scanning a stdio MCP server means actually running it, the tool uses a consent gate in interactive mode — it asks before connecting to each server and records user_declined for anything you skip. Secrets found in configs are redacted before analysis hits the network. Remote requests to link-local and cloud-metadata addresses are blocked.
For CI pipelines, --ci exits non-zero when findings remain, so you can add a scan step to a pre-deploy job or a cron run.
The honest caveat
You need a Snyk account and a free API token to get any analysis at all. Set SNYK_TOKEN before running or it won't start. The free tier is there, but it's a signup gate — and Snyk's README explicitly says bulk use of the standard API is treated as abuse, so it's not something you'd drop into an org-wide automated pipeline without a paid plan.
The CLI output format is also labeled experimental, meaning Snyk reserves the right to change field names and output structure between releases. Don't write scripts that parse specific JSON keys unless you're pinning the version.
Windows coverage is patchy: Claude Desktop skills aren't scanned at all on Windows, and Claude Code connector discovery is listed as unverified.
export SNYK_TOKEN=your-api-token-here
uvx snyk-agent-scan@latest
Built and maintained by Snyk. github.com/snyk/agent-scan. 3.2k stars, MIT licensed.